

Apple has patched a critical macOS Screen Sharing vulnerability after attackers exploited internet-facing Macs to gain root access and install Monero mining software, according to an updated warning from the Netherlands’ National Cyber Security Centre.
Summary
- Apple patched CVE-2026-65400 after attackers exploited Mac Screen Sharing services to install Monero miners remotely.
- Dutch cybersecurity officials confirmed compromised Macs had root access and unauthorized Monero mining software installed.
- CISA now scores the authentication flaw 9.8 critical, up from its earlier 7.1 assessment overall.
- Huntress found tens of thousands of potentially exposed Macs, especially internet-hosted bare-metal Apple systems worldwide.
- Changing Screen Sharing passwords cannot fix the flaw; affected Macs require Apple security updates immediately.
The Dutch NCSC updated its advisory on Aug. 12 to confirm active exploitation of CVE-2026-65400 on multiple systems with port 5900 exposed to the internet. In every reported case, attackers obtained root access and installed a Monero miner. The agency did not disclose how many Macs were compromised or identify the attackers.
Apple Screen Sharing flaw bypasses authentication
Apple patched CVE-2026-65400 on Aug. 6 in macOS Tahoe 26.6.1, Sequoia 15.7.9 and Sonoma 14.8.9. The company described it as an authentication flaw caused by improper state management that could allow an attacker on the network to access Screen Sharing without valid credentials.
Security firm Huntress found that the flaw affects the Secure Remote Password authentication process used by macOS Screen Sharing. Its analysis showed an attacker could cause the service to treat an unauthenticated connection as authenticated and obtain privileged access.
Because exploitation occurs before normal authentication, Huntress said changing a Screen Sharing password, disabling legacy VNC authentication or removing authorized user accounts does not address the vulnerability. The recommended fix is installing Apple’s latest security update or disabling Screen Sharing until the system can be patched.
Tens of thousands of Macs may have been exposed
Huntress researcher Ryan Dowd said a Censys search identified “tens of thousands of potentially vulnerable hosts.” That estimate covers Macs that appeared exposed to the internet and should not be interpreted as tens of thousands of confirmed compromises.
The risk is particularly relevant to hosted bare-metal Macs, including Mac minis rented for remote workloads. Huntress said some hosting environments expose Screen Sharing services on newly provisioned machines, increasing the attack surface when systems have not yet received Apple’s Aug. 6 patches.
The flaw now carries a 9.8 critical CVSS score from CISA’s vulnerability analysis, with no privileges or user interaction required under its current assessment. The National Vulnerability Database shows that CISA upgraded the scoring on Aug. 14 after initially assigning a lower severity assessment.
Hackers used compromised Macs to mine Monero
The Dutch cases involved cryptojacking rather than reported theft of wallet credentials. Attackers used the compromised Macs’ computing resources to mine Monero after obtaining root control. The NCSC has not disclosed the mining software, pool addresses, attacker wallets or resulting XMR proceeds.
Monero has repeatedly appeared in cryptojacking campaigns because it can be mined using general-purpose computing hardware. As crypto.news previously reported, a Darktrace investigation found malware quietly deploying cryptocurrency mining software after attackers gained access to Windows systems.
Apple devices have also faced other crypto-related malware campaigns. In related coverage,North Korean hackers targeted macOS users with malware aimed at crypto companies using fake meetings and malicious software updates.
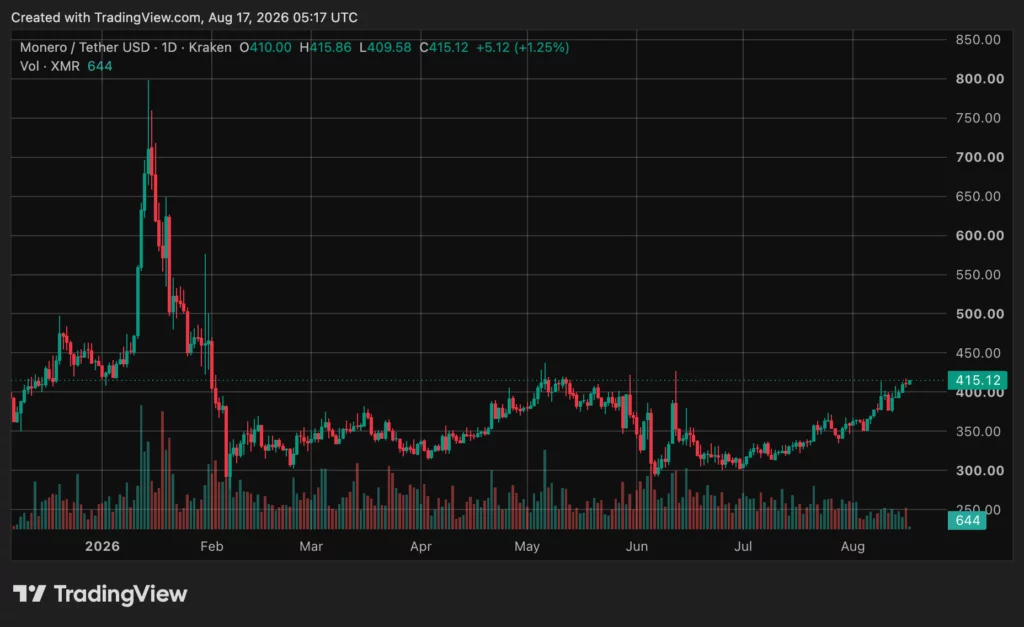
Meanwhile, Monero (XMR) traded at around $414 at press time, indicating less the 1% increase in the past 24 hours and almost 5% in the past 7 days (according to crypto.news market data)
What happens next
The immediate priority is patching Macs running vulnerable versions of Sonoma, Sequoia and Tahoe. Systems exposed directly to the internet through Screen Sharing face the clearest documented risk, although Huntress recommends updating Macs even when administrators believe the service is disabled.
The Dutch NCSC has confirmed exploitation but has not attributed the campaign or published indicators identifying the Monero mining infrastructure. Further disclosures from incident responders could clarify how widespread the attacks became before Apple’s Aug. 6 fix.
